When the fridge becomes the entry point: locking down IoT after Europe's cold-chain attacks
By Camille Campbell, Senior Director of WWAN and security product marketing for Ericsson Enterprise Wireless Solutions
Thursday, 19 November, 2026
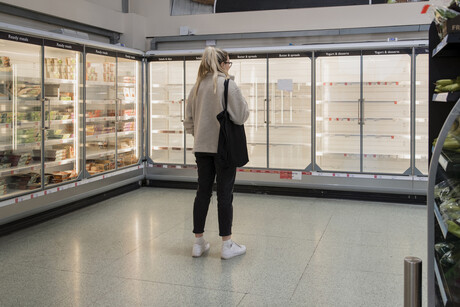
Overnight on 11 October, attackers remotely took control of commercial refrigeration controllers at hundreds of supermarkets across France, forcing units into a continuous defrost cycle and driving temperatures as high as 50°C. Stores threw out stock, some equipment caught fire, and retailers estimated losses in the tens of millions of euros. Three weeks later, a second wave hit supermarkets in Sweden, Belgium, Luxembourg, Ireland, Estonia and other European countries.
These attacks exposed a much broader enterprise security challenge: connected devices that keep businesses running are not always protected by the same security controls as traditional IT systems. From refrigeration units and building controls to cameras and connected vehicles, these devices can create vulnerabilities that turn a seemingly isolated security breach into a costly operational disruption.
Zero-trust networking for IoT devices
Devices like these were never built to defend themselves, so the network has to do it for them. Where an organisation is running distributed operations, every distributed sensor, controller, sign, camera or vehicle expands the attack surface, and a single exposed or compromised device can become an entry point. Ericsson’s NetCloud Secure Connect replaces legacy Virtual Private Networks (VPNs) and private Access Point Names (APNs) with a policy-governed, zero-trust architecture that can be orchestrated from the WAN edge to the cloud. Key zero-trust features include:
- Resource definition: Connected IoT devices and private applications are dark until explicitly defined, so a controller is not discoverable simply because it has been plugged in. In addition, all IP addresses are cloaked, ensuring that nothing is discoverable through an IP scan or exposed to the Internet.
- Deny-all-by-default access: Instead of starting with broad network access, where every authorised user or IoT device can reach all the resources on a network or network segment, policies are built to restrict access — enabling only what is needed.
- Default blocking of east/west traffic: Unlike traditional VPN and routed networks, Secure Connect can prevent damaging propagation of breaches by restricting all east/west traffic and blocking all incoming connections to a site, vehicle or IoT device by default.
For enterprise networks, these controls mean IoT devices reach only the services they need, devices are not exposed to the internet, lateral movement is constrained and breaches can be contained to their origin. Network controls are not a substitute for patching and supported firmware, but they remove the kind of direct internet exposure that Europe’s recent breaches demonstrate that operators need to eliminate.
Resilient connectivity for distributed IoT assets
The Ericsson Cradlepoint S400 is a semi-ruggedised 5G router that brings zero-trust connectivity with NetCloud Secure Connect to diverse IoT use cases. Compact and field-expandable, it supports additional interfaces for serial devices, GPIO connectors and extra Ethernet ports — ideal for digital signage, building automation and light industrial sensors. Some European retailers are already modernising their connections: after the French incident, Sweden’s Coop said it was moving store systems from 4G to 5G networks and modern modems.
For enterprise IT teams, the challenge is deploying and maintaining large numbers of devices across many sites while minimising field service visits. NetCloud Manager simplifies large-scale deployments and lifecycle operations by centralising orchestration, policy distribution, firmware management and eSIM capabilities. It also enables centralised visibility and management with advanced location services for simple asset tracking, geofencing and AI insights. In addition, Cellular Intelligence features including Cellular Health Events Monitoring correlate signal trends with carrier tower and band changes, reducing on-site testing, accelerating time-to-repair and helping to maintain service levels for critical applications like cold-chain monitoring, connected point-of-sale and security cameras.
Compared to private APNs — which also create a secure, segregated network pathway for cellular devices — Secure Connect is a more cost-effective, faster-to-deploy and self-managed option. Ericsson offers a multi-year subscription for its cellular IoT routers, such as the Cradlepoint S400 that includes Secure Connect, compared to paying for the setup of a private APN plus monthly charges.
Key benefits of Ericsson Secure Connect
- ‘Connect and go’ zero-trust security: With powerful orchestration and intuitive bulk provisioning, new sites, vehicles and IoT devices can be securely deployed in just a few clicks, achieving both agility and security.
- Flexible deployment options: Secure Connect can be consumed as a service or deployed on-premises by deploying a service gateway in a data centre or virtual private cloud environment.
- Higher scale and capacity: The on-premises service gateway supports 10 times more tunnels and four times more capacity than Ericsson’s traditional VPN headend. The cloud-delivered option offers true pay-as-you-grow scaling.
- Resources must be defined before they are accessible: Rather than new applications or IoT devices being instantly visible and accessible the moment they are network connected, in a Secure Connect network, resources must be explicitly defined before they can be accessed or seen by anyone or anything.
- AI-driven insights: AIOps dashboard for key insights plus an AI-based Virtual Expert who can answer queries, generate graphs and assist with troubleshooting.
Where to start
The advice from agencies and analysts following the European attacks is consistent: identify which IoT controllers are on your network, check whether any are reachable from the internet, confirm they run supported, up-to-date firmware and replace default credentials. Where a device cannot be patched or retired immediately, isolating it is the next best step. Deloitte’s Frank Groenewegen noted that disconnecting exposed controllers doesn’t fix the root cause, but it does stop an attacker reaching them.
The European refrigeration attacks showed how quickly an ordinary, overlooked, connected device can become an operational crisis. For enterprises building out IoT, the combination of Ericsson’s Cradlepoint S400 router with NetCloud Manager and NetCloud Secure Connect offers a security-first, operationally efficient foundation. By embedding zero-trust principles at the edge, simplifying routing and policy management and automating cellular performance monitoring, organisations can connect more of the business with confidence — keeping operations running, systems more reliable and costs under control.
[On-Demand Webinar] Transform from Security Awareness to a Security Culture : A Vital shift for the Finance Sector
Hear from experienced technology and risk leaders on strengthening your security posture,...
Why cyber resilience is at the heart of business continuity in the AI age
As our reliance on cloud services, hybrid environments, and generative AI deepens, protecting our...
Preparing for the post-quantum world: what IT leaders need to know
Experts at DigiCert's recent World Quantum Readiness Day event are urging ANZ organisations...